


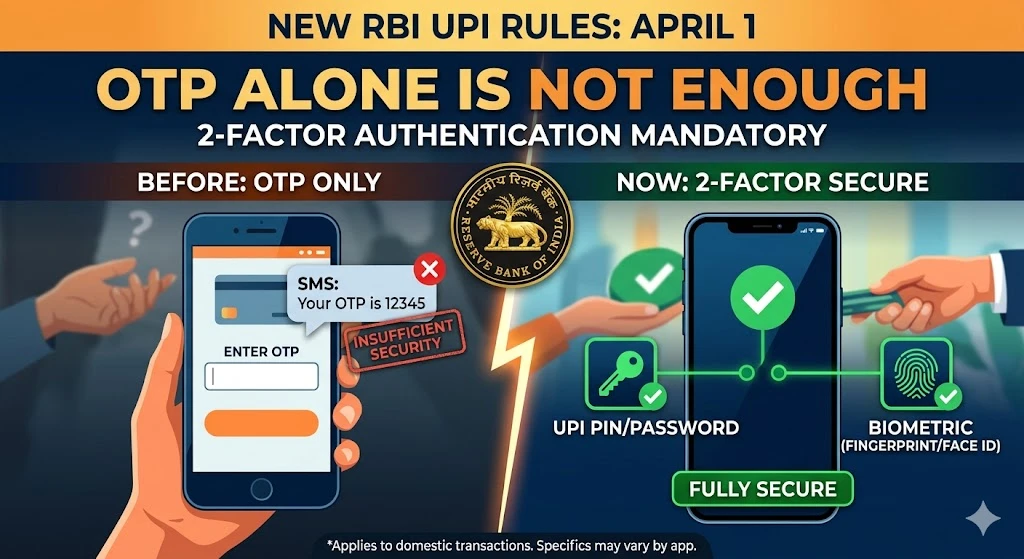
இன்னிக்கே Live — April 1 முதல் UPI Rules மாறிடுது!
GPay, PhonePe, Paytm use பண்றீங்களா? இன்னிக்கு முதல் payment experience change ஆகுது. Reserve Bank of India (RBI) mandatory two-factor authentication (2FA) rules for all digital payments இன்னிக்கு April 1, 2026 முதல் effective.
OTP — registered phone-க்கு வரும் 6-digit code — மட்டும் போட்டா transaction complete ஆகாது. Second verification layer இப்போ mandatory.
Rumour இல்லை, "soon" இல்லை — இன்னிக்கே live. என்ன நடக்குதுன்னு clearly explain பண்றோம்.
Two-Factor Authentication என்னன்னு? — Simple Explanation
Two-factor authentication என்பது — payment confirm பண்றதுக்கு இரண்டு different ways-ல் identity verify பண்றது. பழைய system-ல் OTP மட்டும் போதும். அது problem-ஆ இருந்தது.
SIM swap attack: Fraudster உங்கள் number-ஓட duplicate SIM வாங்கி, OTP intercept பண்றாங்க. Phishing: Fake site-ல் OTP enter பண்ண trick பண்றாங்க. இந்த attacks India-ல் widely happen ஆகுது.
RBI-ஓட new rules இதை fix பண்றது — இரண்டு different categories-ல் verify பண்ணணும்:
Something you know: UPI PIN, banking password, transaction password.
Something you have: Registered device, hardware token.
Something you are: Biometrics — fingerprint scan, face recognition.
Important: இரண்டு factors-ல் ஒன்னு dynamic-ஆ இருக்கணும் — அந்த specific transaction-க்கு uniquely generated, reuse பண்ண முடியாது. OTP technically dynamic-தான், ஆனா single factor-ஆ போதாது. அதோட second layer வேணும்.
UPI Users-க்கு Specifically என்ன Change?
Trusted device-ல் routine UPI transactions — Swiggy order pay, bill split, regular contacts-க்கு send — immediately dramatic-ஆ different feel ஆகாது. Risk-based approach apply ஆகும் (இதை கீழே explain பண்றோம்).
Difference notice ஆகும் situations:
New device-ல் login: GPay, PhonePe new phone-ல் install பண்ணுங்க, verification stricter. OTP-ஓடு கூட biometric அல்லது device authentication step வரும்.
High-value transactions: ₹5,000-₹10,000-க்கு மேல் transfers-ல் additional verification trigger ஆகும். Exact threshold bank-ஓட implementation-ப்படி vary ஆகும்.
Unusual behaviour: Unusual location, unusual time, never-paid payee — extra authentication step வரும்.
Online card payments: Flipkart, Amazon India, Myntra-ல் debit/credit card transactions — OTP + PIN mandatory now all platforms-ல்.
Risk-Based Approach என்னன்னு?
Every transaction-லயும் two steps mandatory இல்லை — risk-based system. Transaction-ஓட risk level-ப்படி security checks scale ஆகும்.
Low risk (known device, small amount, familiar payee): Minimal friction, standard verification.
Medium risk (slightly unusual, moderate amount): OTP + PIN அல்லது biometric required.
High risk (new device, large amount, new payee, unusual location): Stricter — OTP + biometric + confirmation.
Bank மற்றும் payment app background-ல் risk score calculate பண்றது. Score பாக்க முடியாது, ஆனா extra steps-ல் feel ஆகும்.
என்ன Exempt-ஆ இருக்கு?
Recurring e-mandates exempt: Netflix, Amazon Prime, Spotify auto-debit, SIP mutual fund, loan EMI — இவை as usual continue ஆகும். New 2FA rules apply ஆகாது.
Small value transactions (roughly ₹500 or under) — lighter verification under risk-based approach possible.
RBI ஏன் இப்போ இதை பண்றது?
India digital payment fraud numbers sharply climbing. UPI fraud cases, SIM swap attacks, phishing scams targeting Indian bank customers — all increased as UPI adoption grew. OTP-only system known vulnerabilities fraudsters systematically exploit பண்ணாங்க.
UPI global-ஆ expand ஆகுது. NPCI other countries-க்கு UPI take பண்றது. Globally positioned payment system-க்கு global security standards வேணும்.
இப்போவே என்ன பண்ணணும்?
1. UPI apps-ல் biometrics enable பண்ணுங்க. GPay, PhonePe, Paytm Settings → Biometric Authentication ON. Fingerprint அல்லது face unlock enable பண்ணுங்க. இதுதான் most convenient second factor.
2. Registered mobile number active-ஆ, current-ஆ இருக்கணும். SIM old-ஆ இருந்தா, number recently change பண்ணியிருந்தா bank-ல் update பண்ணுங்க.
3. Different PINs use பண்ணுங்க. UPI PIN, banking password, phone unlock PIN — separate-ஆ வையுங்க.
4. Banking apps update பண்ணுங்க. All major banks new rules comply பண்றதுக்கு updates push பண்ணியிருக்காங்க. Old version-ல் இருந்தா update immediately.
5. Extra steps-க்கு panic ஆகாதீங்க. சில transactions கொஞ்சம் longer ஆகும். Intentional. ₹50,000 fraud prevent பண்ற 5-second extra step worth it.
TamilTech-ஓட கருத்து
இந்த change long overdue. OTP-only security always weak link-ஆ இருந்தது — SIM swaps மட்டும் thousands of Indians-ஐ lakhs fraud பண்ணியிருக்கு. New framework payments harder-ஆ பண்றதில்லை, fraud harder-ஆ பண்றது. Yes, occasional transactions few extra seconds. That's the cost — ஒரு country-ல் digital payment fraud real மற்றும் growing threat-ஆ இருக்கும்போது. Payment apps-ல் biometrics enable பண்ணுங்க — இன்னிக்கே. That's the single most practical thing right now.



கருத்துகள் (0)
Be the first to comment!