


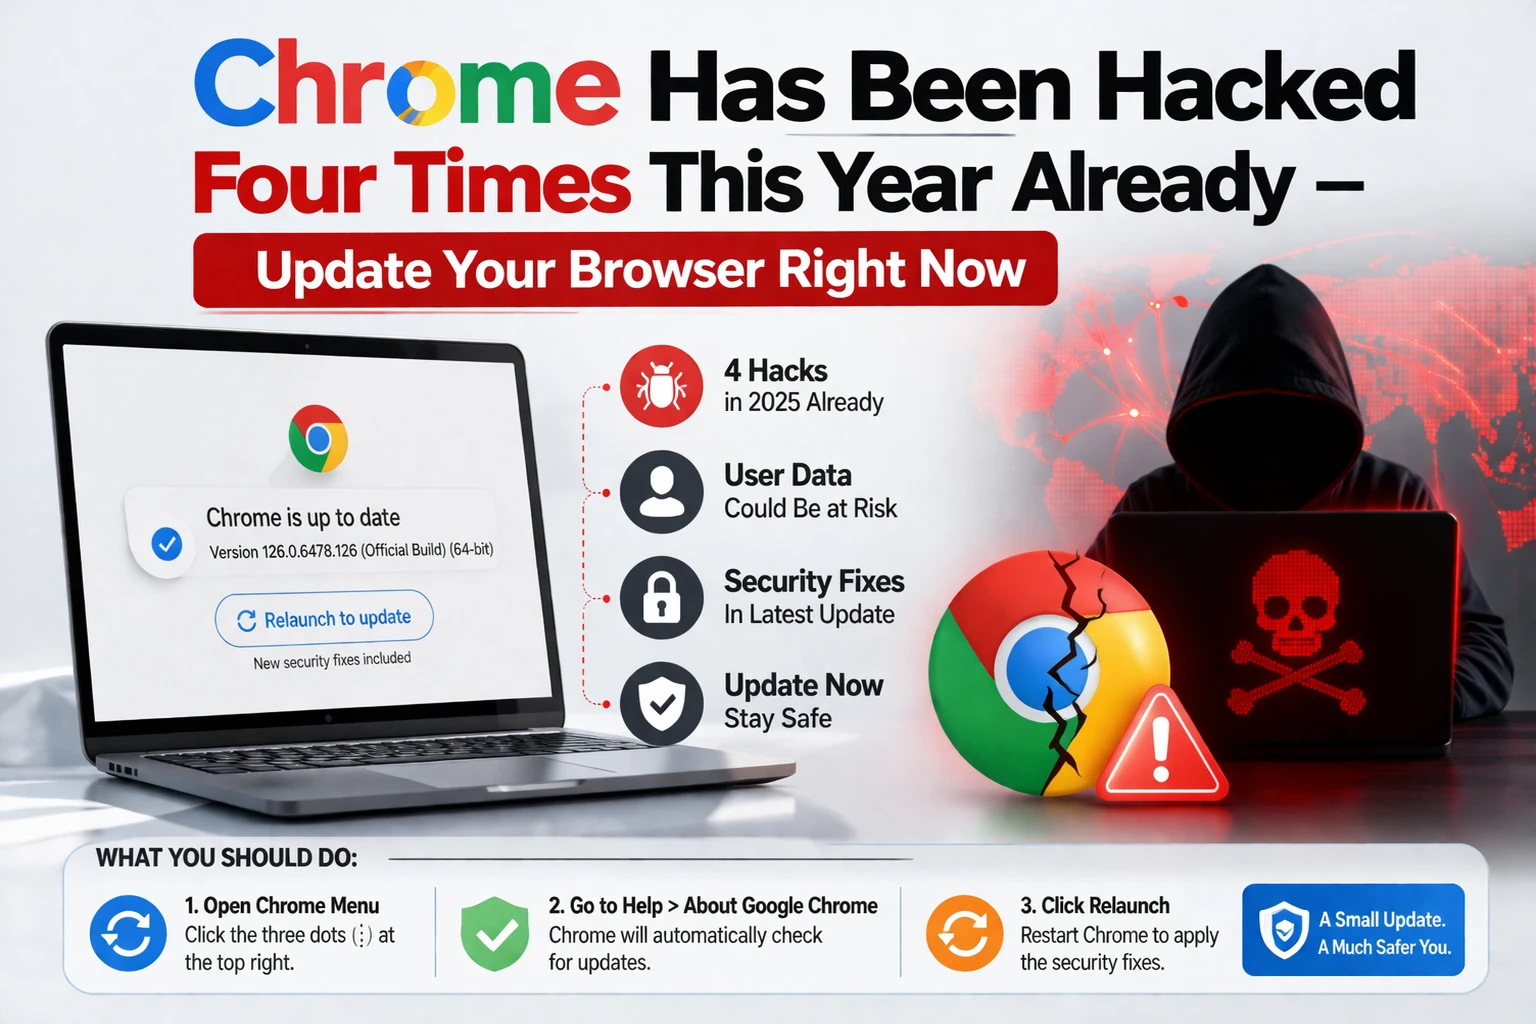
Four zero-days in three months — that's a bad pattern
Let's be direct about what's happening here. A zero-day vulnerability means hackers found a security flaw and started exploiting it before the software company even knew about it. Google has now patched four such flaws in Chrome in 2026 — and we're only in April. That's not normal. In all of 2025, Google fixed eight Chrome zero-days for the entire year. At the current 2026 pace, that number will be exceeded by mid-year.
The latest flaw, officially tracked as CVE-2026-5281, was discovered in Dawn — the graphics component Chrome uses to implement WebGPU. If that sounds technical and abstract, here's what it means practically: this vulnerability exists in the part of Chrome that handles how web pages render graphics and 3D content. An attacker who exploits it can crash your browser, corrupt data on your device, or in the worst cases, execute malicious code on your computer without you doing anything except visiting a compromised webpage.
Google confirmed it has evidence this flaw was being actively exploited in the wild before the patch was released. Translated: real hackers, targeting real users, were using this vulnerability in actual attacks. Google hasn't disclosed details of who was targeted or how — which is standard practice when patches are rolling out — but the emergency update release speed tells you they considered this serious.
What exactly is a use-after-free vulnerability?
The CVE-2026-5281 flaw is classified as a "use-after-free" bug. This is one of the most common and dangerous categories of memory vulnerabilities in modern software. Here's how to understand it without a computer science degree.
When a program like Chrome is running, it constantly allocates and frees chunks of memory to handle different tasks — loading a page, running JavaScript, rendering an image. A use-after-free bug happens when a piece of code tries to use a block of memory after it's already been freed and potentially reassigned. It's like ripping out a page from a book, giving that paper to someone else to write on, and then your original code trying to read what it thinks is still its original page.
For attackers, this creates a window to inject malicious data into that freed memory space before the original code tries to access it. If successful, they can redirect program execution to their own code — effectively taking over that part of the browser's behavior. Combined with other techniques, this can lead to full browser compromise or worse.
The four Chrome zero-days of 2026 — a timeline
This isn't an isolated incident. Here's the complete picture of Chrome zero-days in 2026 so far. The first, CVE-2026-2441, was patched in mid-February — an iterator invalidation bug in how Chrome handles CSS font feature values. Technical and obscure, but still exploited in the wild.
The second and third came in March — CVE-2026-3909, an out-of-bounds write in Chrome's Skia graphics library (the component that actually draws everything you see on screen), and CVE-2026-3910, an inappropriate implementation bug in Chrome's V8 JavaScript engine (the component that runs JavaScript on every webpage). Two zero-days patched in the same month.
Now, in April, CVE-2026-5281 in Dawn — the fourth. The frequency is concerning. Chrome is the world's most-used browser, making it the highest-value target for hackers and nation-state actors who develop these exploits. The sheer scale of Chrome's user base — over 3 billion active users globally — means even a small percentage of unpatched users represents millions of vulnerable machines.
How to update Chrome right now — step by step
Google says the update is rolling out automatically, but "rolling out" doesn't mean it's already on your machine. The safest thing is to manually trigger the update check right now.
On desktop (Windows, Mac, Linux): open Chrome, click the three-dot menu in the top right corner, hover over "Help," and click "About Google Chrome." Chrome will automatically check for updates on that page and install any available update. Once it finishes, click "Relaunch" to restart Chrome with the patch applied. You're looking for version 146.0.7680.177 or 146.0.7680.178 on Windows and Mac, or 146.0.7680.177 on Linux.
On Android: open the Google Play Store, tap your profile icon in the top right, tap "Manage apps and device," then tap "Updates available." If Chrome appears, update it. On iOS, go to the App Store, tap your profile, scroll down to pending updates, and update Chrome if available.
Check the version number after updating by going to the three-dot menu → Help → About Google Chrome. If the version matches the numbers above, you're protected.
Why this matters specifically for Indian Chrome users
India has one of the largest Chrome user bases in the world — hundreds of millions of users across both desktop and mobile. Indian users rely on Chrome for everything: UPI payments through bank websites, filing income tax returns on the IT portal, IRCTC ticket booking, Aadhaar-linked services, online banking, Swiggy and Zomato orders, and workplace tools like Google Workspace.
A compromised browser in this context isn't just a technical inconvenience. If an attacker exploits a Chrome zero-day and gains the ability to intercept or modify what your browser does, they could potentially access active sessions on banking sites, read saved passwords, steal session cookies (which can let them log into sites as you without needing your password), or inject malicious content into pages you trust.
The good news: Google pushed this patch very quickly once aware of active exploitation. The risk window is shortest for users who update immediately. The users most at risk are those running older, unpatched versions of Chrome — particularly on older PCs where automatic updates may not work reliably, or on Android phones where users haven't enabled automatic Play Store updates.
Should you be worried about Chrome's security overall?
Four zero-days in three months sounds alarming. But context matters. Chrome is the most heavily targeted browser in the world precisely because it's the most used. The number of people actively trying to find Chrome vulnerabilities — researchers, bug bounty hunters, criminal hackers, government actors — is proportional to Chrome's market dominance.
The reassuring part is that Google has consistently patched these quickly once discovered. The company's Chrome security team and Threat Analysis Group (TAG) are among the most capable security operations in the industry. The eight zero-days patched in all of 2025 were also addressed rapidly. The system is working — it's just a reminder that "zero exploitable bugs in any software" is not a realistic expectation.
If you want an alternative, Firefox and Safari both have strong security records and zero-day frequency comparable to or better than Chrome. But switching browsers won't eliminate zero-day risk — it just shifts which vendor's zero-days you're exposed to. The practical answer for most users is simpler: keep Chrome updated, enable automatic updates, and don't linger on outdated versions.
TamilTech's take
Four Chrome zero-days in three months is a number worth paying attention to, but not panicking about. The pattern tells us two things: Chrome is being aggressively targeted, and Google is patching quickly when exploits are found. Your job is simple — update Chrome today. Don't wait for the automatic update to arrive on its own timeline. Manually trigger the update check, get to version 146.0.7680.177 or higher, and relaunch the browser. Five minutes of attention right now is worth more than any security software subscription for this specific threat.





Comments (0)
Be the first to comment!