


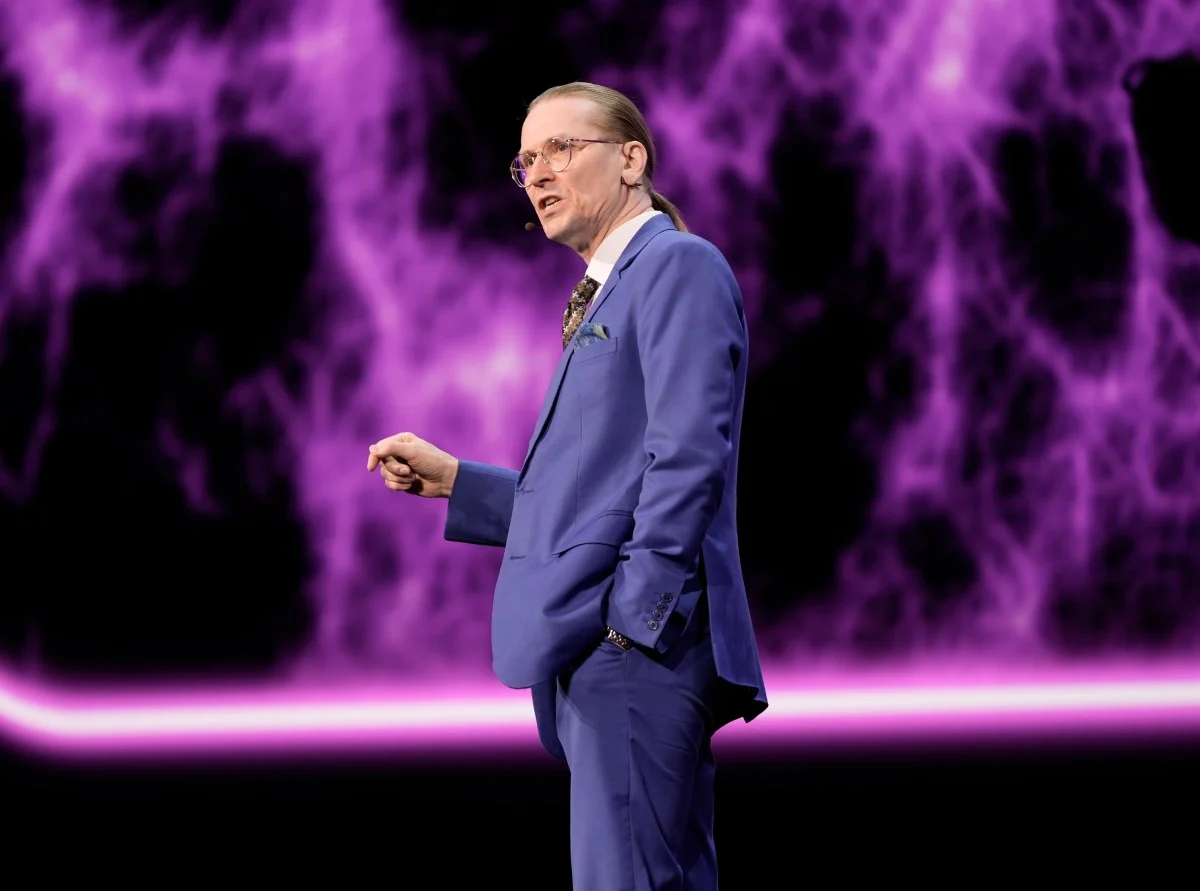
He's seen every kind of cyberattack since the floppy disk era. Now he's worried about something flying over his house.
When Mikko Hyppönen started his career in cybersecurity in the late 1980s, the word "malware" didn't really exist yet. What people called them were "viruses" and "trojans" — and they spread by infecting floppy disks, the physical storage media that people physically handed to each other. The internet as we know it barely existed. A "hacker" was still mostly a term of curiosity rather than threat.
Over the next 35+ years, Hyppönen watched the threat landscape transform completely. He's analyzed thousands of malware strains. He's been a familiar face at every major cybersecurity conference globally — Black Hat, DEF CON, RSA — for longer than most current security researchers have been working. He's the kind of person who can describe the history of computer viruses from personal experience, not from textbooks.
Now, at a stage of his career where most people would be consolidating existing expertise, Hyppönen has pivoted toward a completely different threat category: drones. And his reason is personal in a way that makes the pivot entirely understandable.
The cybersecurity Tetris metaphor that explains why security work is invisible
At Black Hat 2025, Hyppönen delivered a keynote where he used a Tetris analogy to describe the nature of cybersecurity work that's worth understanding. In Tetris, when you complete a row, it disappears. The successful rows never accumulate — only the incomplete ones pile up at the bottom. "When you do your job perfectly, the end result is that nothing happens," he told the room.
This is the fundamental PR problem of cybersecurity as a profession. When a bank's security team successfully stops a breach, nobody writes a headline about it. The attacks that don't succeed don't make the news. What gets reported are the failures — the data breaches, the ransomware attacks, the infrastructure takedowns. Security professionals spend careers defending against threats that the public never hears about because the defense worked.
For 35 years, Hyppönen has been playing that game. The malware he stopped doesn't make headlines. The analysis he completed, the attacks he detected, the threats he documented — much of it is invisible to the general public even as it shaped how the industry operates today.
Why drones, and why now
Hyppönen is Finnish. He lives approximately two hours from Finland's border with Russia. That geographic context matters enormously for understanding why drone security has become his new focus.
Russia's 2022 full-scale invasion of Ukraine changed how military experts, security researchers, and civilian populations near Russia's borders think about drones. The Ukraine conflict has demonstrated, more clearly than any previous conflict, the battlefield dominance of unmanned aerial systems. Drones have been used for reconnaissance, targeted strikes, and psychological pressure at a scale that traditional anti-aircraft systems weren't designed to counter at low cost. The majority of casualties in certain phases of the conflict have reportedly come from drone attacks.
For someone living two hours from a border with an increasingly hostile state that has demonstrated both the will and capability to use drone warfare extensively, this isn't an abstract geopolitical analysis. It's a personal risk assessment. Hyppönen has decided he can contribute meaningfully to the emerging field of drone security — using the same fundamental skills of vulnerability analysis, system exploitation research, and security architecture that he built over 35 years of malware work.
The skill transfer is more direct than it might initially seem. Drones are, at their core, embedded computing systems with wireless communication protocols, firmware that can have vulnerabilities, command-and-control channels that can be intercepted or spoofed, and software that can potentially be exploited. These are exactly the categories of problems that malware researchers understand deeply. The physical hardware is different. The underlying attack surface analysis methodology is familiar.
What drone hacking actually means
Drone security research — which Hyppönen's pivot represents — involves several distinct areas that have emerged as critical vulnerabilities in commercial and military drone systems.
RF (radio frequency) spoofing is one primary attack vector. Commercial drones rely on GPS signals for navigation and positioning. GPS signals can be spoofed — false signals transmitted to deceive the drone into believing it's in a different location. A spoofed drone can be redirected away from its target, made to land in an unintended location, or confused into lost-connection behavior. Israel reportedly used GPS spoofing to divert commercial flights during the Iran conflict escalation. The same technique applies to drones.
Protocol vulnerabilities in drone communication channels are another major area. Many commercial drones use communication protocols that weren't designed with security as a primary consideration — they were designed for low latency, long range, and reliable signal, with security added as an afterthought. Researchers who work on protocol security find these systems familiar and vulnerable in predictable ways.
Firmware exploitation is a third area. Drones run embedded software that can have the same kinds of vulnerabilities — buffer overflows, authentication bypasses, insecure update mechanisms — as any other software system. Malware researchers who've spent decades analyzing embedded systems and finding ways to execute unauthorized code have directly transferable skills for this work.
The India dimension: why drone security matters here too
India has a complicated and rapidly evolving drone security challenge. The Line of Control with Pakistan has seen drone-based intrusions for smuggling, weapons drops, and surveillance — a pattern that's been escalating for years. The 2021 Jammu Air Force Station drone attack was the first drone-based attack on Indian military infrastructure. Since then, the Indian military has been accelerating its counter-drone capabilities while simultaneously developing its own drone fleet.
On the civilian side, India's drone industry has grown rapidly. Under the government's PLI scheme for drones, Indian companies like ideaForge, Garuda Aerospace, and Throttle Aerospace are building commercial drone fleets for agriculture, surveillance, logistics, and infrastructure inspection. DGCA regulations for drone operators are evolving, and the commercial drone sector is increasingly integrated into industrial and agricultural workflows.
The security of these commercial drone systems matters. A poorly secured agricultural drone fleet is a potential surveillance or disruption tool. A logistics drone with exploitable firmware is an attack vector. The skills that Hyppönen is developing — and that he'll presumably share through conference talks, research papers, and potentially industry tools — are skills that India's growing drone security community needs.
DRDO and the Indian Army are actively working on counter-drone systems. But the cybersecurity community's involvement in drone security — understanding vulnerabilities, developing detection systems, hardening firmware — is equally critical and currently underserved in India.
The broader pattern: security skills going where the new threats are
Hyppönen's pivot is part of a broader pattern in security research. As digital threats have multiplied and the security industry has professionalized, veterans of earlier threat categories increasingly move toward new attack surfaces that are adjacent to their expertise but where the security community hasn't yet built deep knowledge.
Hardware security researchers who started on PC firmware vulnerabilities moved into IoT security as that attack surface emerged. Network security veterans moved into cloud security. Malware analysts moved into mobile security. The same skill transfer logic applies to physical autonomous systems — drones, self-driving vehicles, industrial robots — which are all embedded computing systems running wireless communication stacks that security researchers understand how to analyze.
Hyppönen's name recognition and three-decade track record means his entry into drone security will bring attention and credibility to the field in a way that a newer researcher couldn't. When he presents drone vulnerability research at Black Hat or DEF CON, the audience will take it seriously.
TamilTech's take
The Hyppönen story is interesting precisely because it demonstrates what genuine expertise looks like when it meets a new problem domain. Thirty-five years of malware analysis isn't just technical knowledge — it's a way of thinking about adversarial systems, attack surfaces, and defense architecture that applies beyond software. Drones are just the next generation of networked, hackable computers with wings. That the person who analyzed floppy disk viruses in 1989 is now the person analyzing drone firmware in 2026 is actually exactly the right progression. India's drone security community, which is growing rapidly under real threat pressure, could use more people making this kind of transition.




Comments (0)
Be the first to comment!