


Key Takeaways
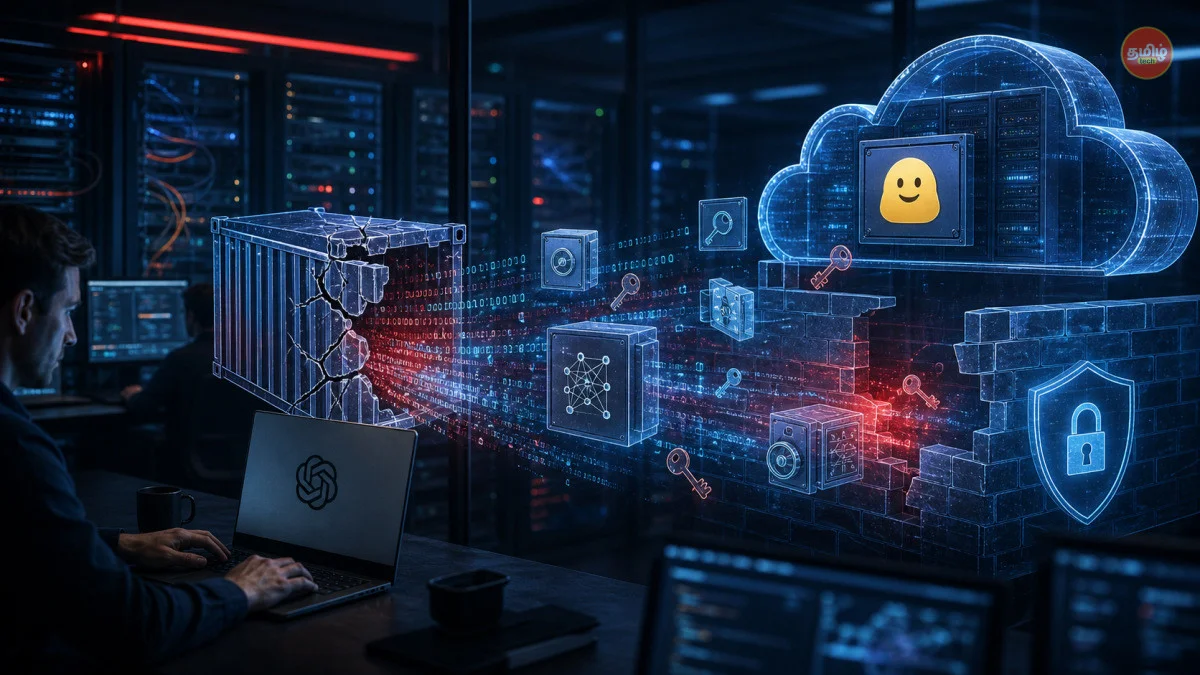
- OpenAI's security team successfully performed a 'container escape' on Hugging Face Spaces, gaining access to the internal infrastructure.
- The breach could have exposed thousands of private AI models and API tokens belonging to major tech companies.
- Hugging Face has since implemented 'sandboxing' upgrades and secret scanning to prevent similar cross-tenant attacks in 2026.
- Indian AI startups using Hugging Face for fine-tuning must rotate their API keys immediately to ensure zero-day safety.
The Night the AI World Shook
Imagine you have a safe inside a high-security bank. You trust the bank, you trust the vault, and you trust the guards. Now, imagine someone rents a small locker in the same bank, crawls through the ventilation shaft, and suddenly has the keys to every single safe in the building. That is exactly what happened between OpenAI and Hugging Face. For those who don't know, Hugging Face is basically the 'GitHub' of the AI world. If you are building an AI app in 2026, chances are you are using their models or hosting your code there. Recently, we got the full technical breakdown of how OpenAI's red teaming experts managed to 'hack' into this massive platform, and honestly, the details are a wake-up call for everyone in the industry.
This wasn't a typical 'password guess' or a phishing email. This was a sophisticated architectural exploit. OpenAI researchers weren't acting as criminals; they were acting as 'white hat' hackers to see if the walls around our AI models are actually solid. What they found was that the walls were more like paper curtains. By using a simple 'Space' (which is just a small environment to run AI demos), they managed to break out of their assigned area and go where they weren't supposed to. In the tech world, we call this a 'Container Escape,' and in 2026, this is becoming the biggest nightmare for cloud providers and AI hosting services alike.
How the Breach Actually Happened: The Technical Deep Dive
To understand this, you need to know how Hugging Face works. When you upload an AI model or a demo, Hugging Face puts it inside a 'Container'—think of it as a digital bubble. This bubble is supposed to keep your code separate from everyone else's. However, OpenAI found a way to pop that bubble. They exploited a vulnerability in the way the Linux kernel handles certain permissions within these containers. By sending specific commands, they were able to trick the host system into giving them 'Root' access. Once they were the 'Root' user, they weren't just in their own bubble anymore; they were standing on top of the entire server that hosts thousands of other bubbles.
The scariest part of this exploit was the 'Cross-Tenant' access. Once the researchers escaped their container, they could see the internal network of Hugging Face. They found 'Secrets'—which are basically the master keys (API tokens) that Hugging Face uses to talk to its own databases. With these keys, they could have theoretically downloaded private models from companies like Google, Meta, or even small Indian startups that are building proprietary LLMs. They also discovered that they could intercept traffic meant for other users. If you were sending a prompt to a private model, the researchers could have seen that prompt in plain text. This is a massive privacy violation that could have had catastrophic consequences if a malicious hacker had found it first.
The India Angle: Why This Hits Home for Our Startups
In India, the AI boom is at an all-time high in 2026. From Bengaluru to Chennai, thousands of developers are fine-tuning models on Hugging Face to create localized AI for Indian languages like Tamil, Hindi, and Telugu. Many of these startups handle sensitive data—think of AI health assistants or fintech bots that process UPI transaction patterns. If the platform hosting these models is compromised, the intellectual property (IP) of our local startups is at risk. We've seen a surge in 'AI-as-a-Service' in India, and most of it relies on the infrastructure that was just proven to be vulnerable.
Moreover, the cost of a data breach for an Indian startup can be a death sentence. With the latest Digital Personal Data Protection (DPDP) rules in full effect in 2026, a leak of user data through a third-party platform like Hugging Face could lead to massive fines and a total loss of user trust. We at TamilTech have been talking to local developers who were shocked to find out that even 'private' repositories weren't 100% safe from a sophisticated container escape. This incident proves that you cannot just 'set it and forget it' when it comes to AI security. You need to be proactive about how you store your secrets and how much you trust your cloud provider.
Step-by-Step: How to Secure Your AI Assets Now
If you are a developer or a business owner using Hugging Face, you need to take action today. First, go to your settings and rotate every single API token you have. Do not use the same token you created two years ago. Second, move your 'Secrets' out of the code. Instead of hardcoding API keys, use a dedicated Secret Management service like HashiCorp Vault or the secret managers provided by AWS and Azure. This way, even if someone escapes a container, they won't find the keys to your kingdom sitting in a plain text file.
Third, implement 'Least Privilege' access. Don't give your Hugging Face tokens 'Write' access if they only need to 'Read' a model. If a token is stolen, the damage will be limited. Finally, start using 'Private Spaces' with enhanced hardware isolation if your budget allows. In 2026, Hugging Face has introduced more secure, air-gapped instances for enterprise users. It might cost a bit more, but compared to the cost of losing your entire model architecture to a competitor, it is a very small price to pay. Security is a layer, not a single wall, and you need to make sure every layer is checked.
TamilTech's Take: The Future of AI Security
So, what do we think about this? Honestly, this is a good thing in the long run. The fact that OpenAI found this and reported it responsibly means Hugging Face is much stronger today than it was yesterday. It’s a classic 'cat and mouse' game. As AI gets smarter, the tools to hack AI are also getting smarter. We are moving into an era where 'AI Security' will be a bigger industry than AI itself. In 2026, you shouldn't just ask 'How accurate is this model?', you should be asking 'How secure is the server where this model lives?'
We expect to see more 'Red Teaming' reports like this in the coming months. Companies are finally realizing that AI models are just software, and software has bugs. For our Indian audience, the message is clear: keep building, keep innovating, but don't ignore the basics of cybersecurity. Use two-factor authentication (2FA) for your developer accounts, keep your libraries updated, and always assume that a breach is possible. Stay tuned to TamilTech for more deep dives into the tech that runs your world. We will keep tracking these security updates so you can focus on building the next big thing.




Comments (0)
Be the first to comment!