

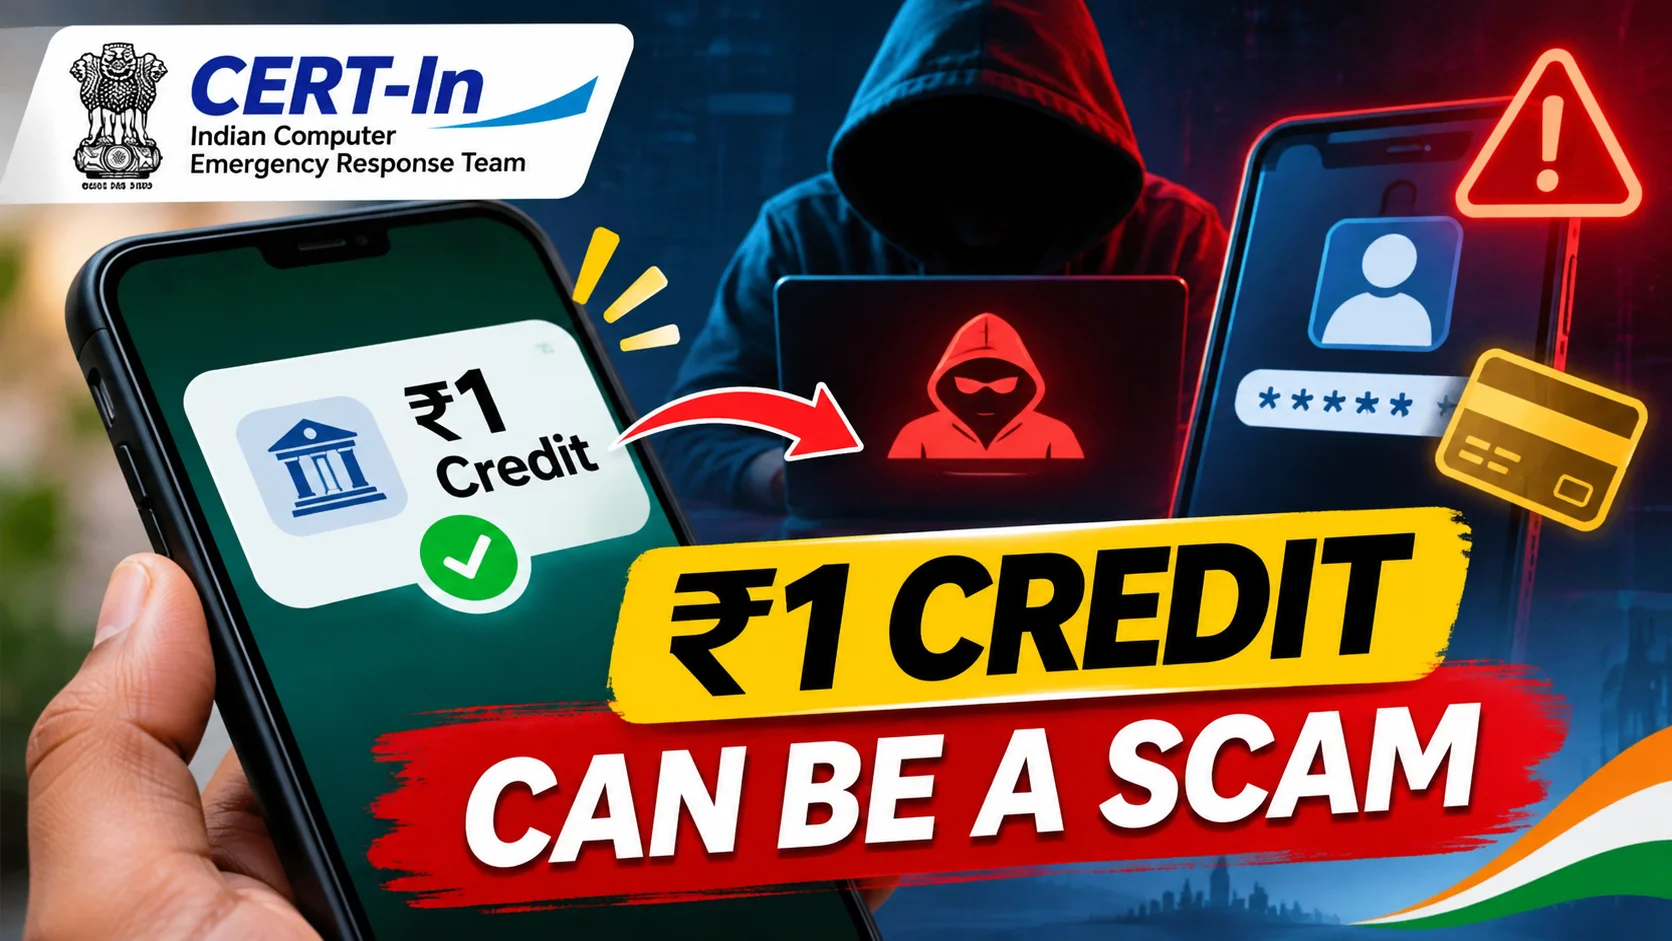
If a rupee just landed in your account from a name you do not know, do not turn CERT-In’s advisory into a personal ghost story. Business Today, updated 5 November 2026 at 10:37 AM IST in Noida, says the Indian Computer Emergency Response Team warned on 4 November about a campaign it calls CRAFTY FALCON. Moneycontrol, published the same morning at 10:37 IST, spells the campaign Crafty Falcon and says the advisory is critical. The target is India’s banking, financial services and insurance stack: NBFCs, fintech companies and payment aggregators. The ₹1 transfer in the warning is a test inside those companies’ payment systems, before a larger unauthorised move. It is not a report that every one-rupee UPI credit on a personal PhonePe or GPay is an AI hacker knocking.
That distinction is the whole point of forwarding this properly. Business Today identifies the advisory as CIAD-2026-0058 and calls the campaign an active, ongoing threat. Moneycontrol says the same timing and the same victims, and adds the detail that makes the headline: hackers performed small-value transactions such as Rs 1 before executing large transfers. A one-rupee ping is how you check whether a payment route works. The theft, if the route works, is the transfer that follows. Neither paper prints a total amount stolen, a list of company names, or a count of customers who lost money. "Hackers steal funds" in Moneycontrol’s headline is the agency’s warning that funds have been moved. It is not a published ledger.
What the campaign is using
Both papers say the attackers are using publicly available AI tools to run attack chains on their own, at machine speed. Business Today names ARTEX, PentAGI, Cairn and CyberStrikeAI. Moneycontrol’s list is the ARTEX family of an LLM-based PentAGI multi-agent penetration system, the Cairn attack engine, and the Cyberstrike AI framework. The tools, as the advisory is quoted, generate and refine tailored scripts quickly and change the payload based on how the target responds. Business Today adds that the supporting infrastructure changes IP addresses within hours or days. That is a description of automation pointed at companies. It is not a shopping list, and it is not something a reader should go install "to see if their bank is safe." A random APK that claims to scan for Crafty Falcon is a more ordinary way to get robbed than a one-rupee credit.
The methods the papers actually name stay at the company layer. Business Today says attackers have used cloud management services such as AWS Systems Manager and Lambda to run commands and drop files, entered production through exposed testing and staging systems using shared credentials, tokens and network connections, altered application packages to make unauthorised API calls, and routed traffic through whitelisted third-party fetchers to get around IP allow-lists. Moneycontrol quotes CERT-In that merchant settlement APIs of payment aggregators were exploited or abused to move funds, and that payment and disbursement APIs were used for unauthorised transfers. Crypto exchanges and virtual digital asset firms were targeted too, with wallet keys stolen and funds siphoned. Newly disclosed file-upload and deserialisation bugs in PHP and Node.js apps were used to drop web shells, Business Today says. None of that is a consumer setting you toggle. It is a company’s cloud, its test environment, its payment API and, in some cases, its crypto wallet custody.
They came back after the fix
This is the line I would not bury. Moneycontrol says companies have been re-targeted despite earlier remediation. Business Today is more specific. Successful attacks have continued, including against NBFCs and fintechs that had already tried to fix the hole. Some were hit again after an incomplete fix, with the activity timed for weekends and holidays, when fewer people are watching. Moneycontrol’s summary says the attacks used autonomous AI during low-monitoring windows. A patch that was announced in a Friday email is not the same as a patch that held through Sunday. CERT-In is telling the institutions that, not announcing that your savings account was emptied.
The advice in Business Today is also aimed at those institutions. Round-the-clock monitoring. Lock down cloud infrastructure. Keep testing environments off the production network. Patch quickly. Flag a ₹1 test transaction to a new beneficiary that is followed by a larger transfer. Put a cooling period on new beneficiaries. Watch for unauthorised AI tools and large language model API usage inside the company. That last item is a corporate control. It is not an order for you to uninstall ChatGPT because a fintech got breached.
What a personal UPI user should actually do
Look at the one-rupee credit the way you already look at a wrong UPI collect request. If you do not recognise the sender, do not tap a link in the SMS that follows, do not call the number in the message, and do not "return" the rupee to a VPA someone messages you. A refund of a mistaken transfer, if you even owe one, goes through your own bank or the app you already have installed, not through a WhatsApp that arrived two minutes later. These articles do not say a ₹1 credit by itself drains an account. They say attackers test a route with ₹1 and then try a larger unauthorised payment on systems they have already broken into. Those systems are NBFC, fintech and payment-aggregator systems.
The consumer habit that still matches the advisory is the new-beneficiary pause. Banks already delay or flag a first transfer to a new account. CERT-In is telling institutions to treat ₹1, then a big transfer, as a pattern, and to cool off new beneficiaries. If your app warns you that a beneficiary was just added, that warning is the useful part. Approving it because a caller says he is from the fraud department is the old scam, and this advisory does not create a new helpline. CERT-In has not, in either story, published a phone number for customers to report a one-rupee credit. Your bank’s in-app support is the place. A number forwarded with the article is not.
I would also not mix this up with yesterday’s other CERT-In notes. The Tata iRA advisory is about vehicle apps. The six-hour AI incident reporting rule is a compliance clock for companies. Moneycontrol mentions both in the neighbourhood of this story. Neither one means your car app or your office chatbot is part of Crafty Falcon. Same agency, different documents.
The version worth sending
On 4 November 2026 CERT-In issued CIAD-2026-0058 on an ongoing campaign called CRAFTY FALCON. It is hitting NBFCs, fintechs, payment aggregators and, in Moneycontrol’s account, crypto firms. Public AI tools are being used to automate the intrusion. One technique is a ₹1 test transfer, then a larger unauthorised payment, including through merchant settlement and disbursement APIs. Some companies were hit again after an incomplete fix, often on weekends and holidays. No stolen-amount total and no customer-by-customer list is in either article. If a rupee arrives from a stranger, leave it alone and do not chase it through a link. The people this advisory is written for are the firms that move the money, and the thing they are being told to watch is a tiny transfer followed by a big one.

Comments (0)
Be the first to comment!