


What’s the fuss about AI‑generated apps?
AI coding assistants like Lovable, Base44 and Replit have turned app‑building into a weekend hobby. You type a prompt, the tool spits out a full‑stack app in minutes, and you’re ready to push it live. Sounds like a dream, right? But the dream has a dark side.
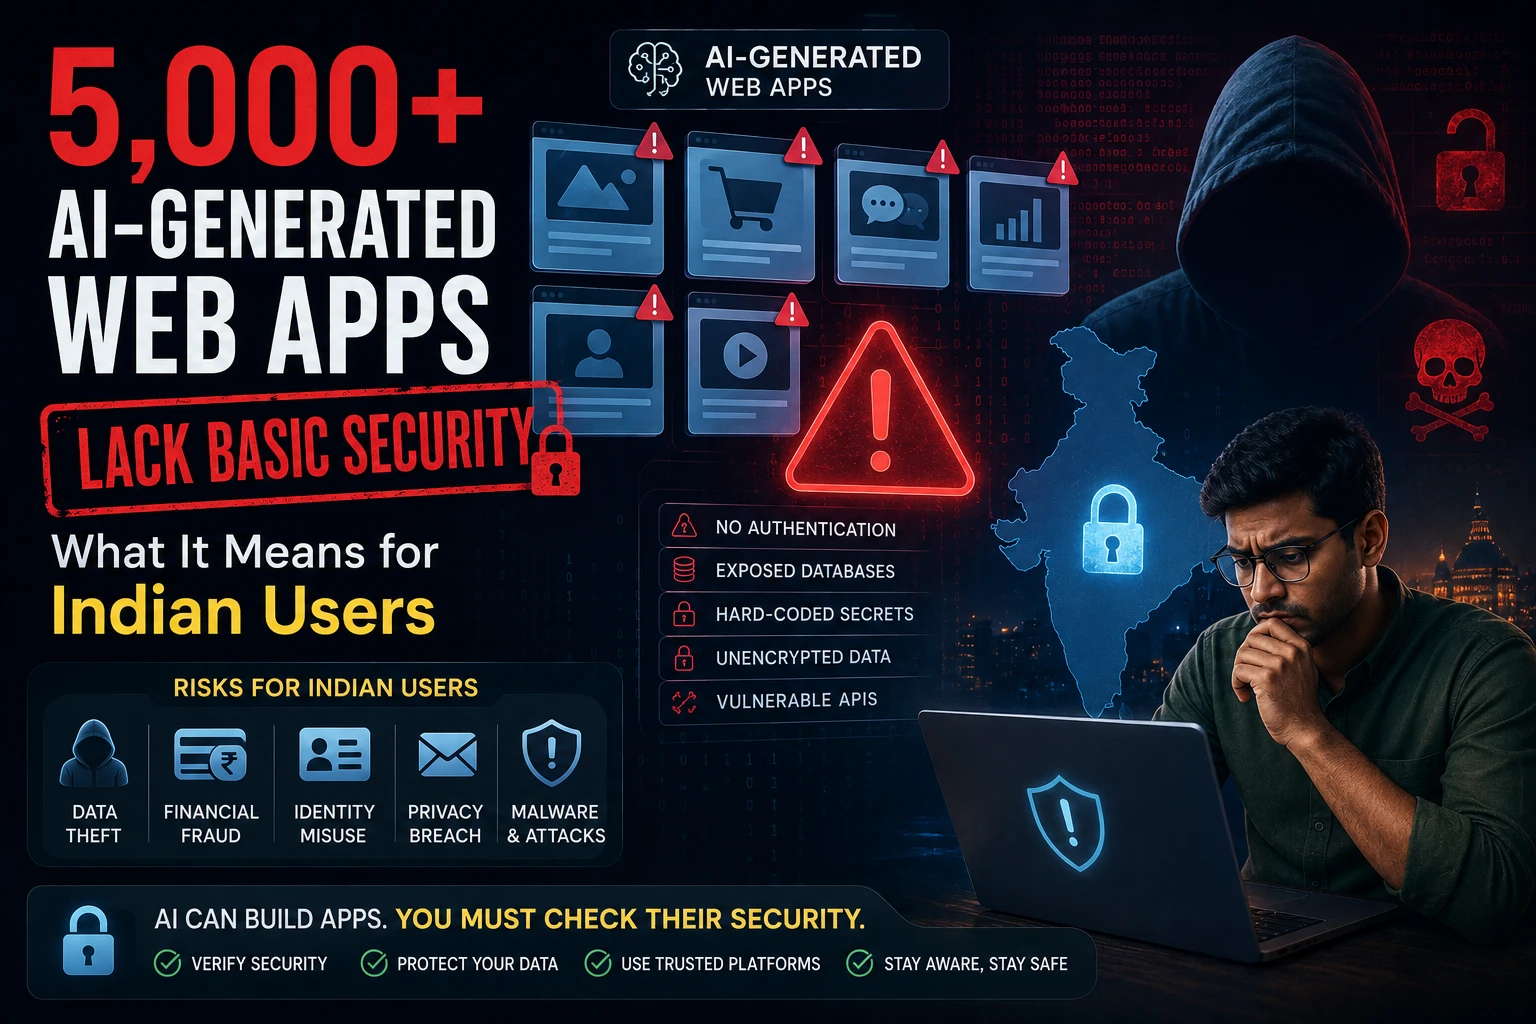
Researchers dug into more than 5,000 of these AI‑crafted web apps and found a shocking trend – most of them either skip authentication entirely or use weak, hard‑coded credentials. Even worse, about 40% of the apps expose API keys, database connection strings or personal data in plain text.
Numbers that hurt
- 5,000+ apps built with AI tools were scanned.
- ~85% had no login or used a default admin/admin combo.
- ~40% leaked sensitive data such as AWS keys, Stripe secret keys, or user emails.
- Only ~10% implemented any form of Two‑Factor Authentication (2FA).
These aren’t just academic findings – they translate into real risks for anyone who clicks on a shiny new startup demo or a freelancer’s portfolio site.
Why Indian users should worry
In India, we love to try out new web services – from a quick UPI payment gateway to a niche SaaS for small retailers. If the underlying app is built by an AI tool without proper security, a hacker can easily scrape the exposed keys and start siphoning money from your bank or stealing personal info.
Imagine you sign up on a new e‑commerce site that promises 0% GST on first purchase. Behind the scenes, the site is running on a Replit‑generated Node.js app with a hard‑coded Stripe secret key. A malicious actor discovers the key, creates fake charges, and your credit card gets blocked. All because the developer trusted an AI‑generated skeleton without adding basic safeguards.
Common pitfalls in AI‑generated code
- No authentication layer: The tool assumes you’ll add login later, but many developers ship the app as‑is.
- Hard‑coded secrets: API keys, DB passwords are often pasted directly into .env files that get committed to public repos.
- Out‑dated dependencies: AI models pull the latest libraries without checking for known CVEs.
- Lack of input validation: SQL injection or XSS vectors are left open.
These issues are not exclusive to AI tools – any novice coder can make them – but the speed of AI generation means they spread faster.
What Indian developers can do right now
Here’s a quick checklist to harden any AI‑generated app before you hit npm start or python app.py:
- Open the project folder and locate the .env file. If you see keys like SECRET_KEY=abc123, replace them with real, randomly generated values.
- Add a proper authentication flow. For Node.js, use passport.js with JWT. For Python/Django, enable the built‑in auth system.
- Enable Two‑Factor Authentication (2FA) for admin accounts. Libraries like authy or django-otp make it easy.
- Run a dependency scanner. Commands like npm audit or pip-audit will flag vulnerable packages.
- Never commit .env or config.json to GitHub. Add them to .gitignore and use GitHub Secrets or Vercel Environment Variables.
Even a simple npm install helmet can add a layer of HTTP header protection against clickjacking and XSS.
What users should look out for
If you’re a regular consumer, here are red flags when you land on a new web app:
- URL looks like app.replit.com or lovable.ai – often a free hosting domain.
- Login page asks for only an email, no password, or uses a default admin/admin combo.
- Site asks for sensitive info (bank details, OTP) without HTTPS – check for the lock icon.
When you see any of these, treat the service as untrusted. Use a disposable email or a virtual card for the first transaction.
TamilTech’s take – is AI‑coding a threat or an opportunity?
We love the democratisation that AI coding tools bring – anyone can prototype an idea in a day. But the rush to launch must be balanced with security hygiene. In India’s fast‑moving startup ecosystem, a single data breach can cost millions in fines and brand damage.
Our view: AI‑generated code is a great starting point, not a finished product. Treat the output as a scaffold, then apply the same security checklist you would for a manually coded app. If you’re a freelancer, showcase the speed of AI generation, but always mention “Security‑hardened version available on request”. That builds trust.
What’s next?
We expect AI coding platforms to embed security best‑practices in the next generation of models – auto‑generating JWT auth, prompting for secret management, and flagging insecure code. Until then, the burden stays on developers and users.
Stay alert, keep your keys secret, and don’t let a cool demo turn into a nightmare.





Comments (0)
Be the first to comment!